CVE-2026-110447: Hunt Collabora CODE Web Shells in Nextcloud
CISA lists CVE-2026-110447 as exploited. Scope the Nextcloud Built-in CODE app, preserve evidence, hunt web shells, and update or remove it safely.
VigilSecureInfo / Security engineering
Technical guides and threat analysis for defending Linux, cloud infrastructure, and detection pipelines.
Explore the knowledge base
Guides, research, and practical steps from the archive.
CISA lists CVE-2026-110447 as exploited. Scope the Nextcloud Built-in CODE app, preserve evidence, hunt web shells, and update or remove it safely.
A practical guide to inventorying, testing, and deploying Amazon Corretto October security updates across Linux hosts, containers, and Java services.
A practical AWS response guide for the eMudhra CA key compromise, covering affected trust roots, service deadlines, certificate-chain validation, and a tested offline triage lab.
Map CVE-2026-111497 exposure across Node.js, Envoy, Python, and PAN-OS, then apply published fixes with a safe offline inventory lab.
Audit Arm64 Wasmtime services for CVE-2026-115893, patch affected Cranelift branches, and validate sandbox controls with a safe offline inventory lab.
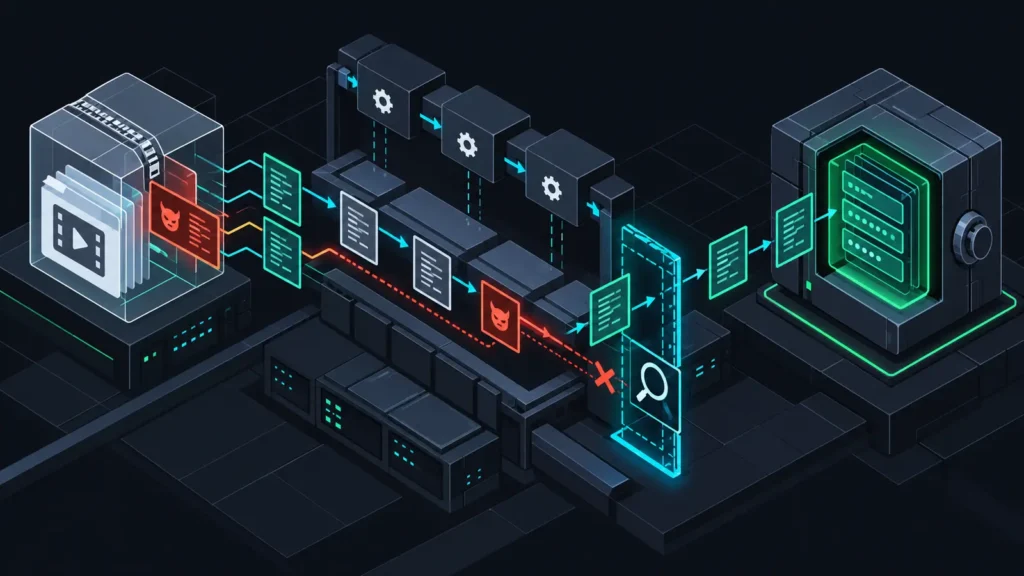
cargo-nextest 0.9.125 through 0.9.149 can execute code from a malicious portable recording. Learn how to find exposure, patch CI runners, detect suspicious builds, and verify the fix safely.
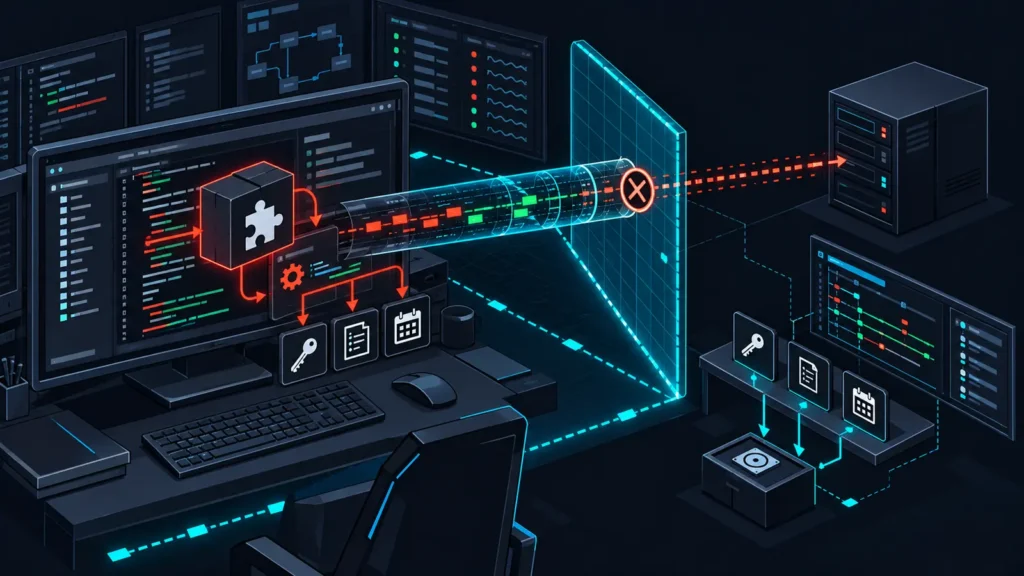
A malicious Claude Code-branded extension from the Cursor Marketplace attempted persistent SSH access. Learn how to scope exposure, preserve evidence, hunt indicators, remediate endpoints, and validate recovery.
CISA added two Ivanti Connect Secure flaws to KEV. Use this defender-focused guide to inventory, preserve evidence, patch, validate integrity, and rotate trust material.