NIST SP 1353 offers a practical way to use generative AI during Cybersecurity Framework 2.0 analysis without pretending that a model is an auditor. The initial public draft, published on August 19, 2026, presents three workflows: governance review, Current State Profile development, and Target State Profile development. Its public-comment period closed on October 15, but the document remains a draft rather than a final standard.
The useful idea is not “let AI do compliance.” It is to use an authorized model as a drafting and correlation tool while preserving source evidence, assumptions, version data, and accountable human review. This guide turns that principle into an operating pattern and a small offline lab that security and GRC teams can reproduce safely.
What NIST SP 1353 actually proposes
The draft applies the CO-STAR prompt structure: Context, Objective, Style, Tone, Audience, and Response. A structured prompt narrows the task and fixes the expected output format. It does not make an answer true. NIST repeatedly separates draft generation from assurance and says qualified personnel must validate scope, inputs, assumptions, applicability, and outputs.
- Governance review: compare policies, strategy, accountability, oversight, and supply-chain context with the CSF 2.0 GOVERN function.
- Current State Profile: map approved artifacts and interview notes to CSF outcomes, cite evidence, and record where sources are silent or thin.
- Target State Profile: draft desired outcomes from mission objectives, risk decisions, requirements, and recognized references.
NIST describes these as notional use cases, not prescriptive assessment or assurance methods. That distinction matters. An AI-generated profile can accelerate a first pass, but it cannot establish operating effectiveness, replace evidence collection, or approve risk on behalf of management.
The control objective: traceable claims, not fluent prose
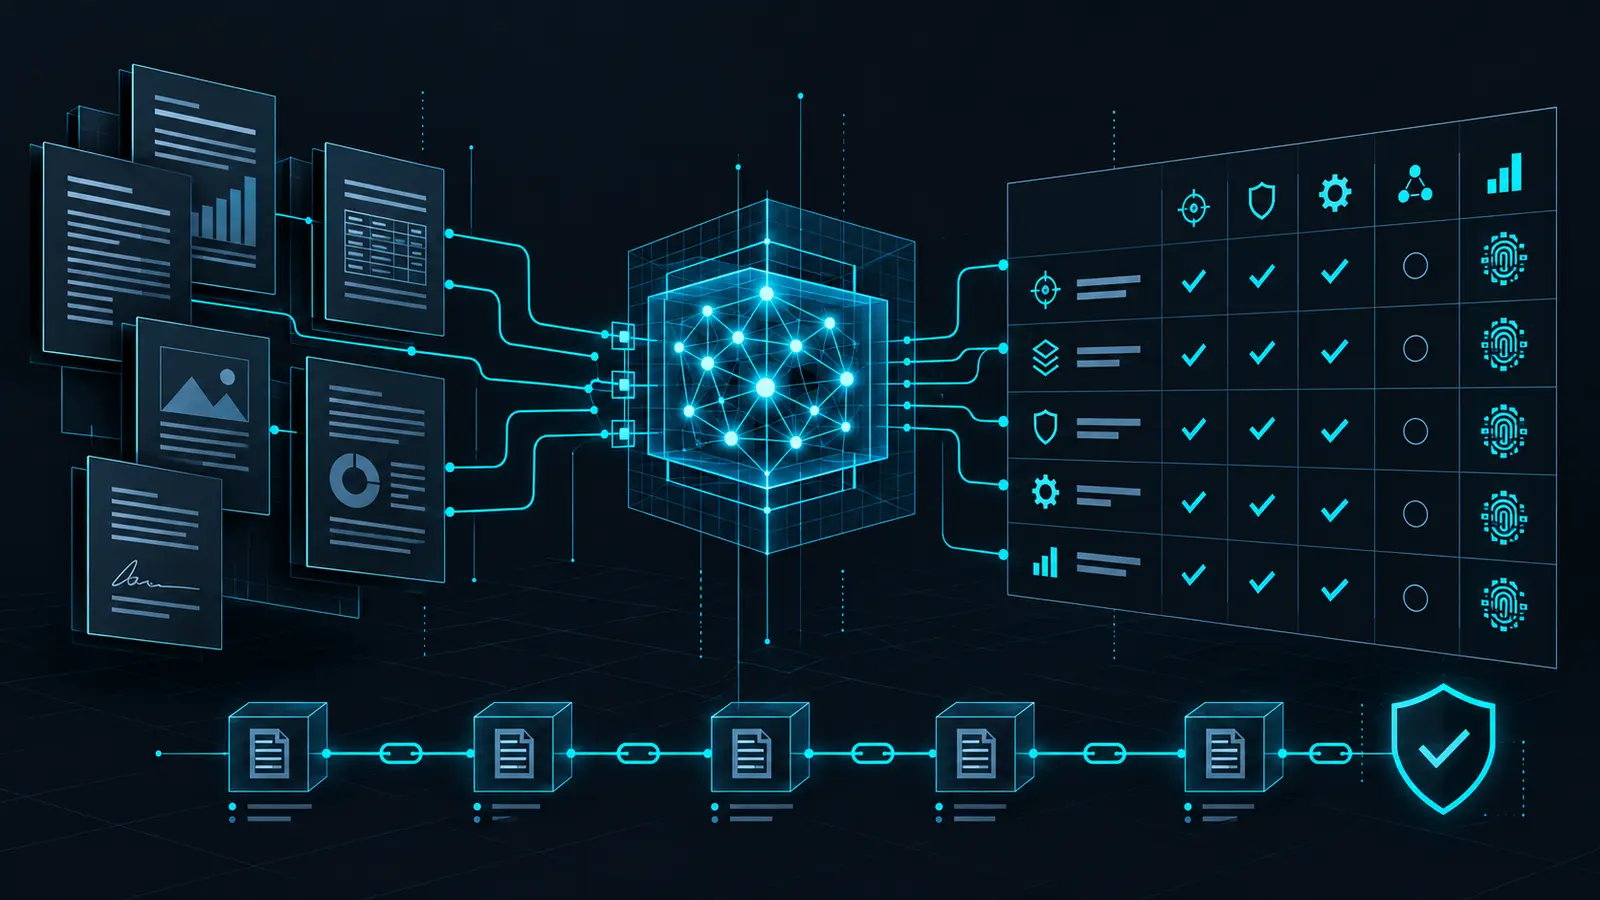
A plausible paragraph is a weak compliance artifact. A defensible assessment row needs a CSF outcome identifier, a clearly bounded claim, an approved evidence reference, a status, an assumption record, and a reviewer decision. If the source does not support the claim, the correct output is “not addressed” or “evidence gap.”
| Field | Why it belongs in the review record |
|---|---|
| CSF outcome | Keeps each statement tied to the CSF Core rather than a generic control theme. |
| Claim | States exactly what the organization says it does. |
| Evidence ID and hash | Links the claim to a fixed, reviewable source version. |
| Status | Separates strength, partial coverage, and a documented gap. |
| Assumption | Exposes inference instead of allowing it to hide inside polished text. |
| Reviewer and decision | Preserves accountability for accepting, revising, or rejecting the draft. |
This complements a broader comparison of NIST, ISO 27001, and SOC 2: the framework defines outcomes, while the assessment process still has to prove what is implemented.
A six-step operating pattern
1. Authorize the tool and the data path
Before uploading anything, document the approved model, tenant, retention settings, training policy, region, access controls, logging, and confidentiality terms. Treat interviews, risk registers, audit findings, penetration-test reports, and system security plans as potentially sensitive. Apply the organization’s data classification and privacy rules first. A privacy-by-design workflow should decide whether data can be submitted, redacted, summarized, or must remain local.
2. Freeze an evidence bundle
Copy only approved artifacts into a case directory. Record a version, collection time, classification, owner, and SHA-256 digest for each file. Hashes do not prove that a policy is correct, but they do show which exact bytes supported a mapping. Keep the original source in the controlled repository; submit a sanitized working copy when possible.
3. Constrain the prompt
Use CO-STAR to state the task and then add hard evidence rules: use only supplied sources, cite an evidence ID for every positive statement, label assumptions, do not invent maturity scores, and return “not addressed” when evidence is missing. Request a machine-readable table in CSF outcome order so reviewers can compare runs.
Context: Analyze the approved evidence bundle against NIST CSF 2.0.
Objective: Draft a Current State Profile for the listed outcomes.
Style: Source-grounded, concise, and traceable. Do not infer beyond the files.
Tone: Neutral and technical.
Audience: Security governance and assurance reviewers.
Response: For each outcome return status, claim, evidence_id, quotation locator,
assumptions, and evidence_gap. If evidence is absent, return Not Addressed.
4. Validate structure before meaning
Automated checks should reject unknown outcome IDs, invalid status values, missing evidence files, stale hashes, and positive claims without evidence. This is the cheap validation layer. It prevents malformed output from entering the human review queue, but it does not judge whether the cited text truly supports the claim.
5. Require two human decisions
A control owner should verify operational facts. A security or assurance reviewer should verify the CSF mapping and evidence sufficiency. High-impact gaps, risk acceptance, legal interpretation, and target-state commitments require the organization’s normal approval path. The model remains a drafting assistant, not a decision authority. The same principle applies to agent security controls: authority must be explicit and bounded.
6. Preserve the run record
Store the prompt version, model and service version when available, input manifest, output, validation report, reviewer changes, and final decision. NIST recommends checking that reference data reflects the current published version. A later rerun should not silently overwrite the record that supported an earlier risk decision.
Hands-on lab: validate a synthetic CSF evidence bundle
This isolated lab does not call an AI service and uses only fictional data. It demonstrates the deterministic gate that should sit between AI-generated profile rows and human review. The script was executed with Python 3.12.14 during preparation of this article.
Prerequisites and setup
- Python 3.9 or later; no external packages.
- A disposable directory on a workstation or test VM.
- No production documents, credentials, personal data, or confidential findings.
mkdir -p csf-lab/evidence
cd csf-lab
printf '%s\n' \
  'SYNTHETIC LAB DATA' \
  'The security steering committee reviews business context and risk assumptions annually.' \
  'The policy does not state who approves changes between scheduled reviews.' \
  > evidence/governance-policy.txt

printf '%s\n' \
  'SYNTHETIC LAB DATA' \
  'The asset inventory job runs daily and records owner, environment, and last-seen time.' \
  'Failed collection jobs create an operations ticket.' \
  > evidence/asset-inventory.txt

cat > profile.csv <<'CSV'
outcome,status,evidence_file,claim
GV.OC-01,Partial,governance-policy.txt,Organizational context is reviewed annually
ID.AM-01,Strength,asset-inventory.txt,The asset inventory is updated daily
PR.AA-01,Gap,,No approved evidence was supplied
CSV
Create the validator
#!/usr/bin/env python3
import argparse, csv, hashlib, pathlib, re, sys

ALLOWED_STATUS = {"Strength", "Partial", "Gap"}
SECRET_PATTERNS = {
    "private key": re.compile(r"-----BEGIN (?:RSA |EC |OPENSSH )?PRIVATE KEY-----"),
    "AWS access key": re.compile(r"\bAKIA[0-9A-Z]{16}\b"),
}

def sha256(path):
    digest = hashlib.sha256()
    with path.open("rb") as handle:
        for chunk in iter(lambda: handle.read(65536), b""):
            digest.update(chunk)
    return digest.hexdigest()

parser = argparse.ArgumentParser()
parser.add_argument("--evidence-dir", required=True, type=pathlib.Path)
parser.add_argument("--profile", required=True, type=pathlib.Path)
args = parser.parse_args()
root = args.evidence_dir.resolve()
errors = checked = 0

with args.profile.open(newline="", encoding="utf-8") as handle:
    rows = csv.DictReader(handle)
    required = {"outcome", "status", "evidence_file", "claim"}
    if not required.issubset(rows.fieldnames or []):
        print("ERROR profile.csv is missing required columns")
        sys.exit(2)

    for row in rows:
        checked += 1
        outcome = row["outcome"].strip()
        status = row["status"].strip()
        evidence_name = row["evidence_file"].strip()
        if status not in ALLOWED_STATUS:
            print(f"ERROR {outcome}: invalid status {status!r}")
            errors += 1
            continue
        if status == "Gap" and not evidence_name:
            print(f"PASS {outcome}: gap recorded without evidence")
            continue
        if not evidence_name:
            print(f"ERROR {outcome}: {status} requires an evidence file")
            errors += 1
            continue
        evidence = (root / evidence_name).resolve()
        if root not in evidence.parents or not evidence.is_file():
            print(f"ERROR {outcome}: evidence is missing or outside the evidence directory")
            errors += 1
            continue
        text = evidence.read_text(encoding="utf-8", errors="replace")
        found = [name for name, pattern in SECRET_PATTERNS.items() if pattern.search(text)]
        if found:
            print(f"ERROR {outcome}: possible secret detected ({', '.join(found)})")
            errors += 1
            continue
        print(f"PASS {outcome}: {status} evidence={evidence_name} sha256={sha256(evidence)[:12]}")

print(f"SUMMARY checked={checked} traceable={checked - errors} errors={errors}")
sys.exit(1 if errors else 0)
Save the code as csf_evidence_check.py, then run:
python3 csf_evidence_check.py --evidence-dir evidence --profile profile.csvExpected output
PASS GV.OC-01: Partial evidence=governance-policy.txt sha256=941af31121c1
PASS ID.AM-01: Strength evidence=asset-inventory.txt sha256=e592089fff5d
PASS PR.AA-01: gap recorded without evidence
SUMMARY checked=3 traceable=3 errors=0
The short hashes will change if you edit the sample files. That is expected. A successful run means the rows meet this lab’s structural rules; it does not certify the controls or the semantic accuracy of a mapping.
Troubleshooting and cleanup
invalid status: use exactlyStrength,Partial, orGap.evidence is missing: confirm the CSV filename matches a file insideevidence/.possible secret detected: remove the file from the working bundle and follow the organization’s secret-exposure process if the value is real.
cd ..
rm -r csf-lab
Review checklist before adopting AI-assisted CSF analysis
- The tool and data route are approved by security, privacy, and legal stakeholders.
- Every positive claim points to an exact evidence source and version.
- Missing evidence stays visible; the model is forbidden to fill gaps with assumptions.
- Control owners verify facts and assurance reviewers verify mappings.
- Risk acceptance and target-state commitments remain human decisions.
- The run record preserves inputs, prompt, output, validation, and reviewer changes.
Conclusion
NIST SP 1353 is most useful as a workflow design document. It shows where generative AI may reduce repetitive analysis and drafting, while its warnings point to the controls that keep the result defensible. Start with synthetic or sanitized evidence, demand outcome-level traceability, reject unsupported mappings automatically, and make qualified reviewers accountable for the final profile. That approach can improve assessment throughput without confusing polished output with verified security posture.
Primary sources
- NIST SP 1353 initial public draft record, published August 19, 2026; comments closed October 15, 2026.
- NIST SP 1353 initial public draft PDF, including the three use cases, precautions, and sample workflow.
- NIST Cybersecurity Framework 2.0 resource center.