Microsoft’s Five AI Agent Risk Classes: A Practical Security Control Map
A practical control map for Microsoft’s five AI agent risk classes, with implementation guidance and a safe offline policy-audit lab.
Comprehensive AI Security guides for cybersecurity professionals. Learn how to secure Large Language Models (LLMs) from prompt injection and data poisoning, implement AI governance frameworks, achieve EU AI Act compliance, and defend against AI-powered cyber threats. Covers NIST AI RMF, OWASP Top 10 for LLMs, model security, and enterprise AI risk management for 2026.
A practical control map for Microsoft’s five AI agent risk classes, with implementation guidance and a safe offline policy-audit lab.
Explore GitHub Security Lab’s AI-assisted fuzzing workflow for C/C++, including its coverage loop, crash triage, a safe cJSON lab, and key limitations.
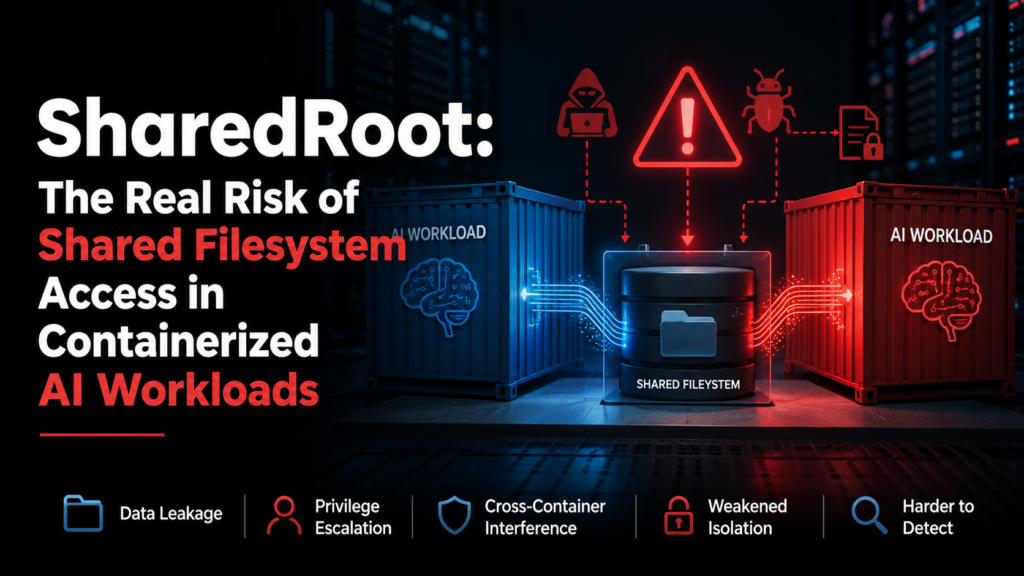
Understand how shared host filesystems and container volumes can expose AI agents to data theft and unintended actions, with practical isolation controls.
AI security 2026: securing LLMs from prompt injection, data poisoning, model theft, OWASP Top 10 for LLMs, NIST AI RMF, EU AI Act compliance, and AI governance.
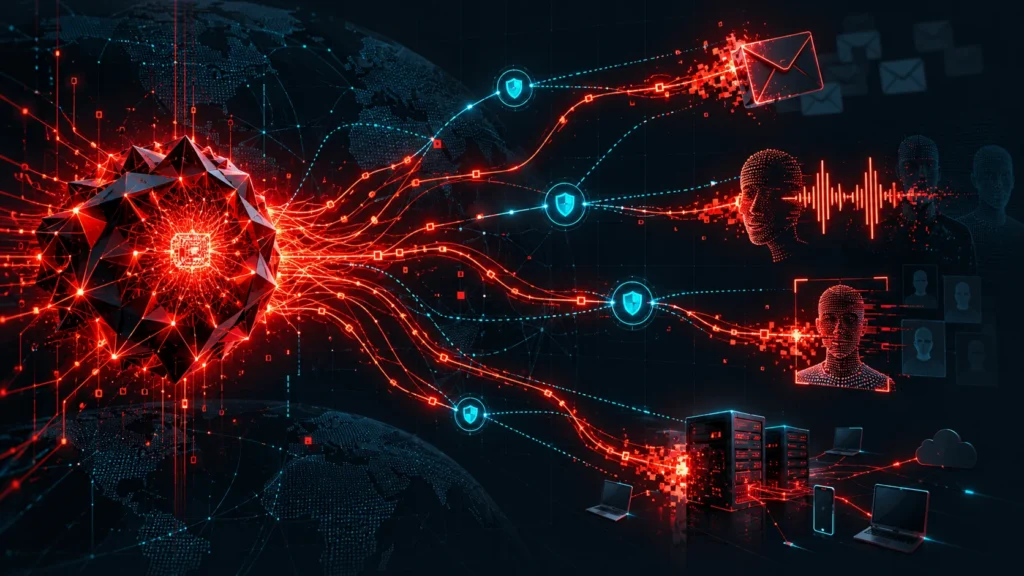
Explore how AI is being weaponized by threat actors and how defenders can leverage AI to stay ahead of sophisticated attacks.