Suricata 8.0.7 Security Upgrade: Validate Rules and EVE Telemetry
A practical SOC guide to upgrading Suricata 8.0.7, validating rules and parsers, checking EVE JSON telemetry, and testing an offline event stream.
Security Operations Center guides covering SIEM deployment, threat hunting, SOAR automation, SOC metrics, and Detection-as-Code for enterprise security operations.
A practical SOC guide to upgrading Suricata 8.0.7, validating rules and parsers, checking EVE JSON telemetry, and testing an offline event stream.
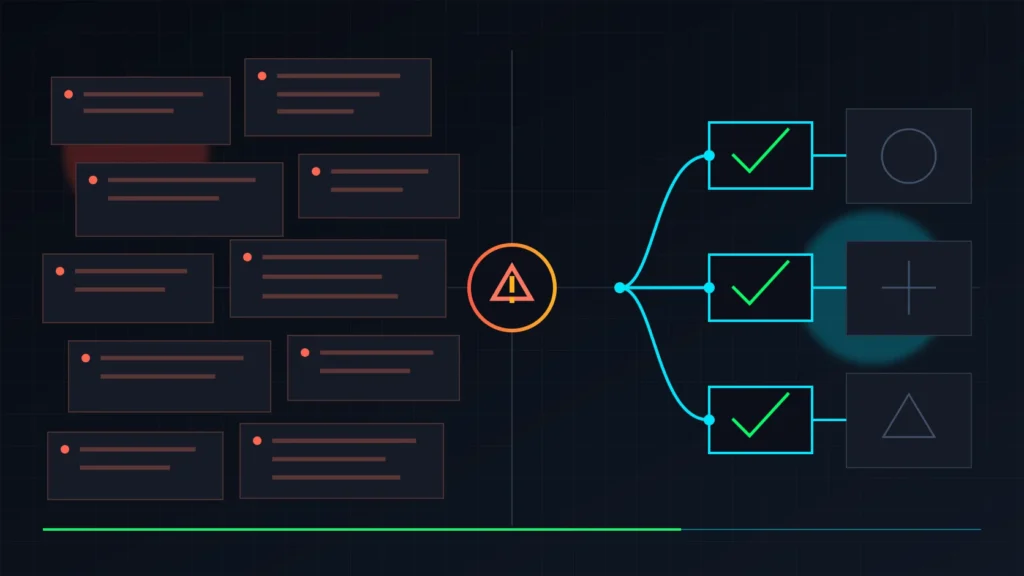
CISA’s Tale of Two SOCs shows why alert tuning, response authority, identity monitoring, and cloud token controls determine whether a SOC stops an intrusion.
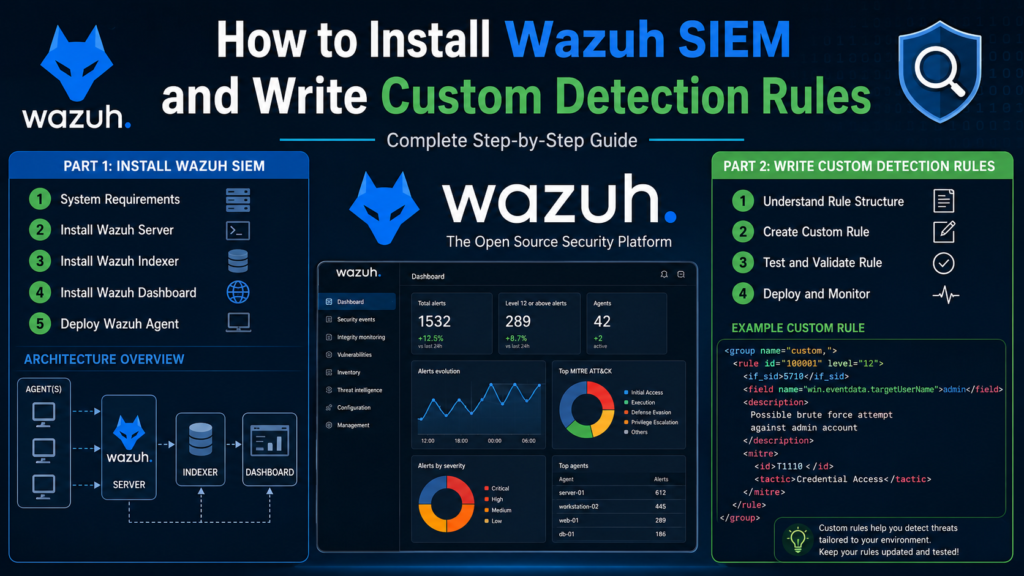
Install Wazuh SIEM on one host, enroll agents, and write custom detection rules that survive upgrades. Step-by-step 2026 tutorial with tested commands.
Advanced SOC operations 2026: proactive threat hunting methodologies, SOAR automation playbooks, Detection-as-Code with Sigma, purple team exercises, and analyst KPI metrics.
Learn how to build, staff, and optimize a Security Operations Center with SIEM, SOAR, and proper alert triage workflows.