Incident brief: CVE-2026-121802 affects the Better Auth Expo integration and can enable account takeover when a server exposes the vulnerable authorization proxy. The fix is not complete until affected packages are upgraded together and the application secret is rotated where the endpoint was reachable.
Better Auth disclosed the underlying issue on November 3, 2026, and the CVE record was published on November 4. The vulnerable component is the @better-auth/expo server plugin. It accepted an OAuth state value supplied by the caller, signed it with the application’s secret, and returned the signature in a cookie without first proving that the server had issued that state.
That boundary failure matters because Better Auth uses the same secret for email verification links and, when enabled, its compact session cookie cache. An unauthenticated attacker who knows a user’s email address could use the signing behavior to authenticate as that user and change the account email. If session cookie caching is enabled, knowledge of a user ID can extend the impact to acting as that user.
What is affected
The vendor advisory says a deployment is affected by the signing issue when its server registers the expo() plugin from @better-auth/expo in an affected version. No wildcard origin is required for this core condition. A separate trusted-origin matching problem requires a wildcard entry such as myapp://* or a wildcard HTTPS subdomain.
| Component | Affected range | Patched floor |
|---|---|---|
@better-auth/expo | >=1.4.0-beta.6, <1.7.16 | 1.7.16 |
@better-auth/expo beta | >=1.8.0-beta.0, <1.8.0-beta.5 | 1.8.0-beta.5 |
better-auth | <1.7.16 | 1.7.16 |
better-auth beta | >=1.8.0-beta.0, <1.8.0-beta.5 | 1.8.0-beta.5 |
At the time of this review, 1.7.17 is the newest stable Expo package. The security floor remains 1.7.16, while 1.7.17 adds a follow-up check that rejects an authorization URL without a state value when the state is stored in a cookie. Teams on the stable line should normally move to the current stable release after validating it, not deliberately stop at the minimum fixed version.
How the authorization proxy crossed a trust boundary
The server signed caller-controlled state
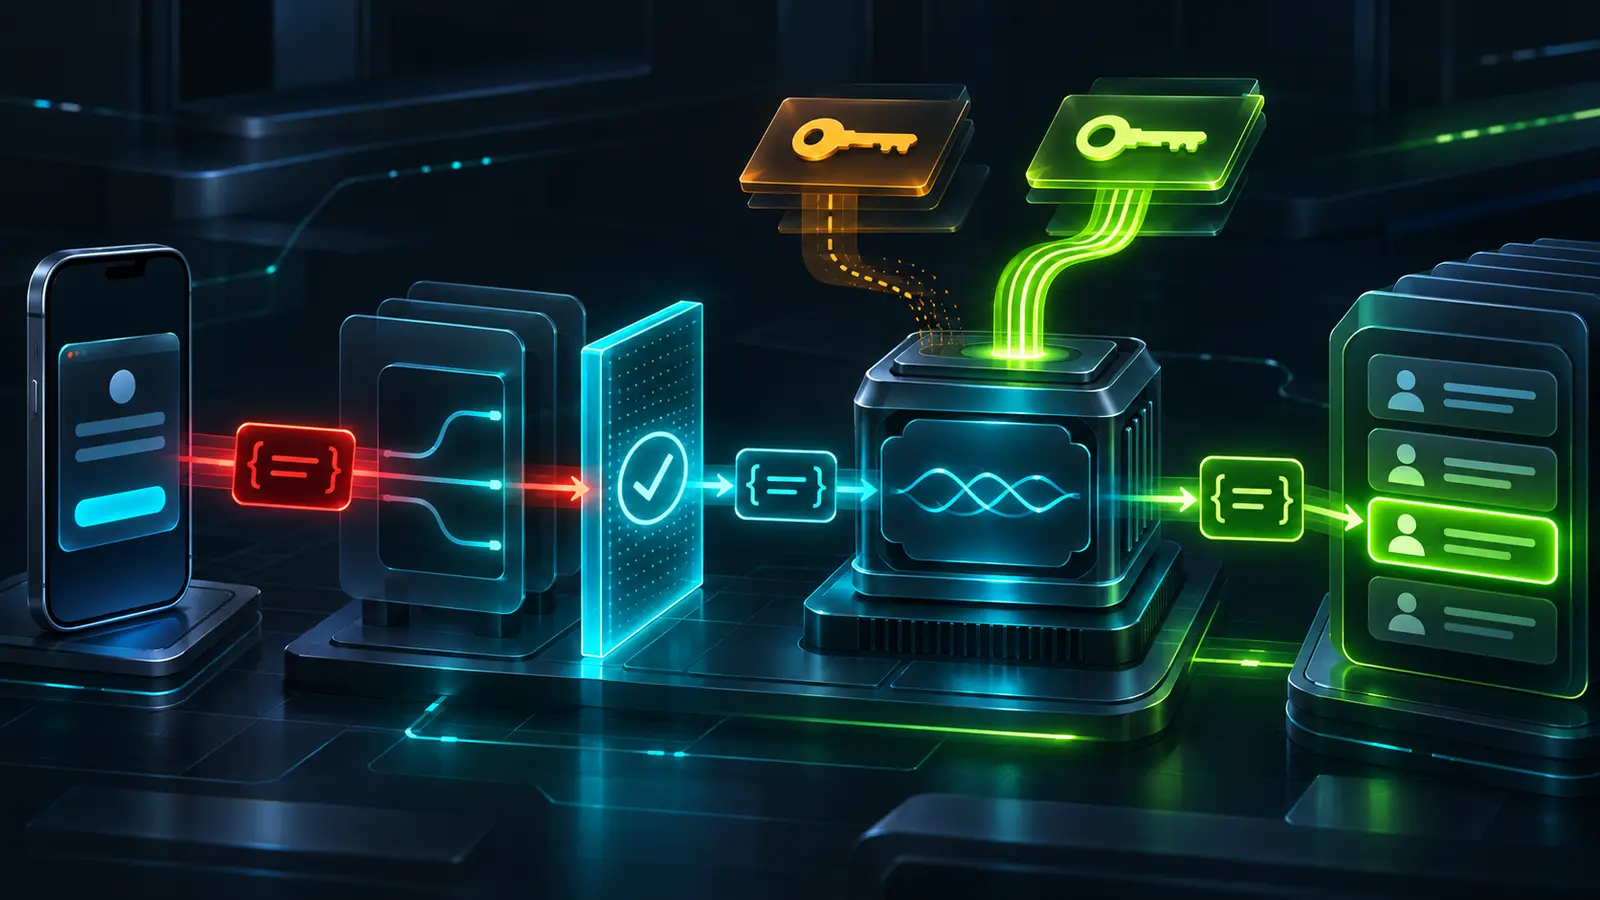
OAuth state is meant to bind the start of an authorization flow to its callback. In this case, the public Expo authorization proxy read state from a caller-supplied authorization URL and placed it into a signed cookie. The signature used HMAC-SHA256 with the application secret.
Signing a value proves only that someone with the key signed it. It does not make arbitrary input trustworthy. If a public service can be asked to sign chosen input, the service has effectively become a signing oracle. The risk became severe because the signature construction and secret were also used for security-sensitive Better Auth artifacts.
Redirect and trusted-origin checks widened the problem
The same endpoint could redirect to an arbitrary external HTTPS site. The vendor also corrected wildcard matching in trustedOrigins so matching now considers the parsed scheme, host and path, and refuses user-info URLs or unparseable values. These are distinct weaknesses, but they reinforce the same lesson: authorization URLs, origins and state must be validated as structured security data, not accepted as convenient strings.
Response plan for security and platform teams
1. Inventory the package and plugin registration
Check every application, worker and shared authentication service. A lockfile may contain several copies, and the vulnerable server can live outside the mobile application repository.
npm ls better-auth @better-auth/expo --all
pnpm why better-auth @better-auth/expo
yarn why better-auth
yarn why @better-auth/expo

# Search server configuration, excluding generated directories.
rg -n --glob '!node_modules/**' --glob '!dist/**'
  'expos*(' .
Record whether expo() is registered, the public auth base path, whether the authorization proxy was internet-reachable, whether the session cookie cache is enabled, and whether production trustedOrigins contains wildcards.
2. Upgrade the package set together
Better Auth packages are released as a coordinated set. Keep better-auth and every installed @better-auth/* package on the same release line. Test in a non-production environment, then deploy all authentication nodes consistently.
# Stable line: install the current stable release after validation.
npm install [email protected] @better-auth/[email protected]

# Beta line: the advisory's fixed beta release.
npm install [email protected] @better-auth/[email protected]

npm ls better-auth @better-auth/expo --all
npm test
If your change policy pins the minimum vendor fix first, use 1.7.16 for both stable packages, then schedule the normal current-release update. Do not mix 1.7.16 and 1.7.17 across Better Auth packages.
3. Rotate the application secret after patching
If the vulnerable endpoint was reachable, rotate the Better Auth application secret after the fixed code is deployed. This ordering matters: rotating first while a vulnerable signing endpoint remains exposed simply presents a new key to the same unsafe behavior. The vendor notes that signatures issued before the fix remain valid until the secret changes.
- Generate a new high-entropy secret using your approved secret manager.
- Update every authentication node atomically or within a tightly controlled window.
- Plan for reauthentication where rotating the secret invalidates signed session material.
- Retire the previous value and confirm it is absent from deployment manifests, CI variables and replicas.
- Record the rotation time so analysts can separate pre-rotation and post-rotation events.
For a broader rotation pattern, see our guide to short-lived GitHub App tokens and secretless CI migration.
4. Tighten origins and preserve valid SSO flows
Remove production wildcards that are not necessary. Better Auth warns that an SSO flow may need the identity provider’s origin explicitly added to trustedOrigins after upgrading. Add only the exact provider origins your deployment uses and test native deep-link, web callback and logout flows.
5. Use workarounds only as a bridge
If the service does not use Expo social sign-in, remove the server-side expo() plugin. If an immediate upgrade is impossible, the vendor suggests blocking requests to /expo-authorization-proxy whose authorizationURL state is not exactly 32 characters from A-Z, a-z, 0-9, - and _. This blocks the signing issue only. It is not a substitute for the full patch, origin corrections and secret rotation.
Detection and investigation
Absence of an alert is not proof that the endpoint was safe. Investigate from the earliest date the affected Expo plugin was deployed through the secret rotation time. Retain raw request data before normal log expiration removes it.
- Requests to the authorization proxy with unusual, repeated or malformed
authorizationURLandstatevalues. - Redirect destinations outside configured identity-provider origins.
- Email-change events shortly after a new session, especially without the normal user journey.
- Sessions created for high-value accounts from new networks or devices, followed by profile or recovery changes.
- Bursts of requests across many email addresses or user IDs.
- Authentication events continuing with old signed material after the patch but before rotation.
Correlate proxy logs, Better Auth application logs, identity-provider events and account-change audit records on a shared timeline. If you already use edge analytics, the workflow in our Cloudflare account-abuse dashboard guide can help organize rate, origin and identity signals. A WAF rule may reduce new attempts, but it cannot invalidate previously issued signatures.
Hands-on lab: classify deployment exposure safely
This lab does not exploit the endpoint, produce signatures or send network traffic. It classifies a synthetic deployment inventory so responders can rehearse triage logic before applying it to real asset data.
Prerequisites and isolated environment
- Python 3.10 or later.
- An empty temporary directory on a workstation with no production secrets.
- No network access is required.
mkdir -p better-auth-triage-lab
cd better-auth-triage-lab

cat > inventory.csv <<'CSV'
service,better_auth,expo_pkg,plugin_enabled,endpoint_public,secret_rotated,wildcard_origin,session_cache
mobile-api,1.7.15,1.7.15,true,true,false,true,true
admin-api,1.7.17,1.7.17,false,false,false,false,false
partner-api,1.7.16,1.7.16,true,true,true,false,false
CSV
Save the next block as classify.py in the same directory.
import csv

def version_tuple(value):
    core = value.split("-", 1)[0]
    return tuple(int(part) for part in core.split("."))

def yes(value):
    return value.strip().lower() == "true"

with open("inventory.csv", newline="", encoding="utf-8") as handle:
    for row in csv.DictReader(handle):
        vulnerable_version = (
            version_tuple(row["better_auth"]) < (1, 7, 16)
            or version_tuple(row["expo_pkg"]) < (1, 7, 16)
        )
        exposed = yes(row["plugin_enabled"]) and yes(row["endpoint_public"])
        rotation_due = vulnerable_version and exposed and not yes(row["secret_rotated"])

        if vulnerable_version and exposed:
            status = "PATCH_AND_ROTATE" if rotation_due else "VERIFY_ROTATION"
        elif vulnerable_version:
            status = "PATCH_AND_CONFIRM_ROUTE_BLOCKED"
        else:
            status = "PATCHED_REVIEW_CONFIG"

        notes = []
        if yes(row["wildcard_origin"]):
            notes.append("review-wildcard-origin")
        if yes(row["session_cache"]):
            notes.append("session-cache-enabled")
        print(f'{row["service"]}: {status}; {",".join(notes) or "no-extra-flags"}')
Run it:
python3 classify.pyExpected output:
mobile-api: PATCH_AND_ROTATE; review-wildcard-origin,session-cache-enabled
admin-api: PATCHED_REVIEW_CONFIG; no-extra-flags
partner-api: PATCHED_REVIEW_CONFIG; no-extra-flags
The script is intentionally conservative and handles only the stable 1.7.x examples shown. For beta releases or a real estate, use a proper semantic-version library and validate the result against the vendor advisory. A patched version does not prove that an exposed secret was rotated, so production inventories should preserve rotation evidence as a separate control.
Troubleshooting and cleanup
- If Python reports that
classify.pyis missing, save the Python block as that filename in the lab directory. - If a version includes a workspace alias or Git URL, normalize it to the resolved package version before classification.
- If output differs, confirm the CSV header and Boolean values are unchanged.
cd ..
rm -r better-auth-triage-lab
What defenders should carry forward
CVE-2026-121802 is a reminder that a cryptographically valid signature is only as trustworthy as the issuance policy behind it. Teams should separate keys by purpose where the framework allows it, keep signing endpoints narrow, validate OAuth state as server-issued and short-lived, and treat redirect destinations as parsed allow-list entries.
For this incident, the response sequence is clear: identify servers registering expo(), upgrade the coordinated Better Auth package set, rotate the application secret when the endpoint was reachable, verify trusted origins, and investigate account and session changes through the rotation boundary. Document each step so an apparently patched service is not mistaken for a fully remediated one.
Primary references
- Better Auth GitHub Security Advisory GHSA-4wq4-2ppv-q3hg, published November 3, 2026.
- Better Auth coordinated security release, November 3, 2026.
- Better Auth v1.7.16 release, November 3, 2026.
- Official Expo package changelog, including the 1.7.16 security fix and 1.7.17 follow-up behavior.
- NVD record for CVE-2026-121802, published November 4, 2026.
- Vercel security bulletin, which notes that WAF protections do not replace patching or secret rotation.