CISA released ScubaGear 2.0 on October 22, 2026, then highlighted the update on October 27. The release changes how Microsoft 365 administrators assess security configuration: the former Defender product is replaced by a broader Security Suite baseline, policy identifiers move, new checks cover risky AI agents and sharing controls, and assessment output is easier to compare over time.
This is not a breach alert or an emergency patch notice. It is a practical guide for using the updated, free assessment tool without confusing a baseline check with automatic remediation or proof of compliance.
What ScubaGear 2.0 does
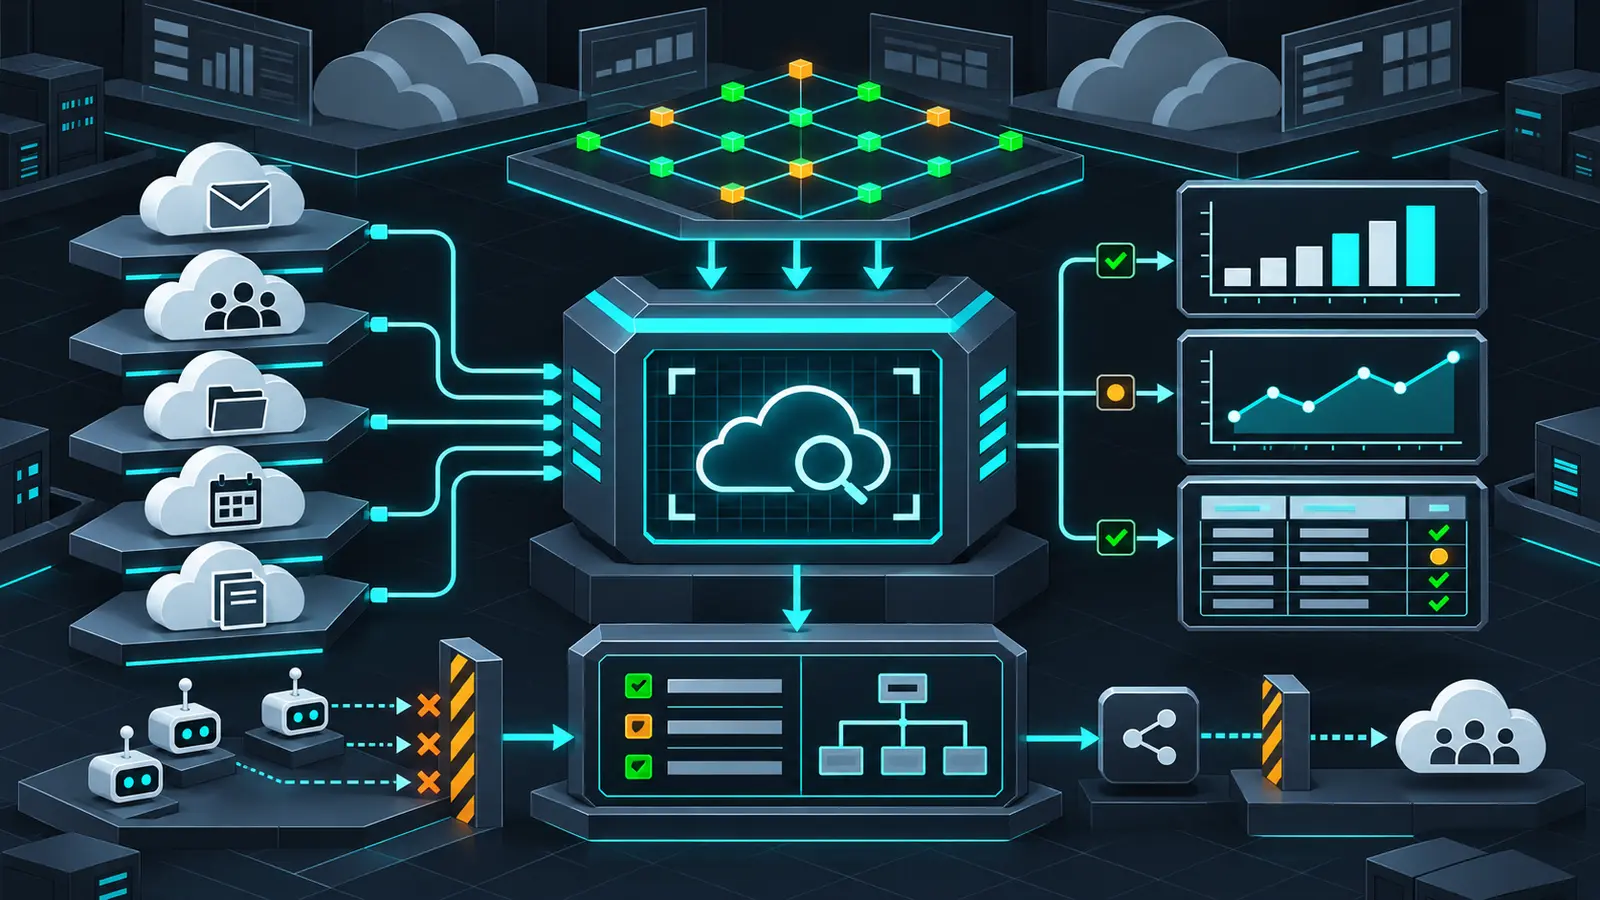
ScubaGear is CISA’s PowerShell-based assessment tool for the Microsoft 365 Secure Cloud Business Applications, or SCuBA, baselines. According to the official documentation, the workflow has three stages:
- PowerShell queries Microsoft 365 APIs for tenant configuration.
- Open Policy Agent evaluates the collected data against Rego policies derived from the SCuBA baselines.
- ScubaGear produces HTML, JSON and CSV reports for review and evidence.
The tool is an assessor. It does not replace change control, license analysis, technical validation or an organization’s risk decision. A failed check can be a real weakness, a licensing gap, an intentional exception, a collection error or a policy that does not fit the tenant’s threat model. Every result needs an owner and evidence.
Why version 2.0 changes existing workflows
Defender becomes Security Suite
ScubaGear 2.0 no longer accepts defender as a product name. CISA consolidated the Defender baseline and selected Exchange Online and Teams policies into securitysuite. Some controls map directly, some split into several new controls, and some were removed. Existing YAML files that reference the old product, a top-level Defender: section, or legacy policy IDs must be migrated before a reliable v2 assessment.
Do not perform a blind search-and-replace across policy identifiers. CISA publishes a migration document and mapping file because one-to-one replacement is not always correct. Preserve the previous configuration and report, update a copy, validate it with v2, and record how every exclusion, annotation or omission moved.
Security Suite checks span several control planes
The new Security Suite baseline brings together advanced threat protection, email protection, data loss prevention, alerting and audit requirements. The v2 release notes identify checks for blocking click-to-run attachments, post-delivery malware handling, malware quarantine or rejection, DLP coverage for sensitive information, required alerts and unified audit logging.
This consolidation is operationally useful because the same outcome may depend on Defender for Office 365, Purview, Exchange Online and Teams. It also means findings should be routed to the service owner who can change the control, not simply to the administrator who ran the tool.
New identity and sharing checks deserve early review
The release adds an Entra policy for blocking risky AI agents. CISA notes that the control depends on Microsoft Entra ID P2 and either Microsoft Agent 365 or Microsoft 365 E7, and that it is not applicable to GCC High or DoD tenants. Treat an unavailable control as a license-and-architecture decision, not an excuse to mark the risk closed.
SharePoint changes include approved-domain or approved-group restrictions for external sharing, expiration of anonymous links at 30 days or less, view-only defaults for anonymous links, and reauthentication requirements for verification-code users. These checks are especially useful when compared with the site’s broader Microsoft 365 security hardening guide.
Plan the assessment before connecting
| Decision | Recommended evidence |
|---|---|
| Tenant and environment | Tenant ID, primary domain, commercial or government cloud, assessment owner |
| Tool provenance | ScubaGear version, module source, dependency versions, collection timestamp |
| Authentication | Approved assessment account or service principal, granted permissions, review date |
| Scope | Products assessed, omitted products, applicable licenses, known collection limitations |
| Risk decisions | YAML exclusions, annotations and omissions with owner, reason and expiration |
| Outputs | Original HTML, JSON and CSV reports plus hashes and protected storage location |
Run the assessment from a dedicated administrative workstation or controlled automation host. Review CISA’s current permissions and network-access documentation before granting access. Separate report collection from remediation: the account used to read settings should not automatically become the account that changes them.
Safe Microsoft 365 assessment workflow
1. Preserve the old baseline
Export the current YAML configuration, note the installed ScubaGear version, and retain the most recent report set. If you previously assessed defender, those files are the evidence needed to explain changes after migration. Hash the files and store them in a restricted evidence location.
2. Install and verify version 2.0
CISA’s quick-start documentation uses the following PowerShell commands. Run them only on an approved workstation after reviewing module provenance and execution policy:
Install-Module -Name ScubaGear
Install-ScubaDependencies
Invoke-SCuBA -Version
The PowerShell Gallery package lists PowerShell 5.1 as the minimum version. Verify that the version command reports 2.0.0 before interpreting v2 policy results. If the workstation already has ScubaGear, use the documented Update-ScubaGear path and review dependency changes instead of mixing module versions.
3. Migrate and validate configuration
Replace the legacy Defender product with Security Suite, move the top-level configuration section, and use CISA’s mapping to review policy IDs. Remove references to policies that the mapping marks as retired. Preserve comments explaining risk acceptance. The configuration validator should report no Defender migration warnings before the production run.
4. Run a read-only assessment
For an initial interactive assessment across all supported products, the official documentation uses:
Invoke-SCuBA -ProductNames *
Get-ScubaGearContext
Confirm the account and tenant immediately after the run. ScubaGear 2.0 requires the -M365Environment parameter for interactive login to non-commercial tenants such as GCC or GCC High; use the value documented for the target environment. Do not interpret a commercial-tenant run as evidence for a government-cloud tenant.
5. Compare, triage and remediate
Version 2.0 adds Invoke-SCuBADiff for comparing two result sets. Use comparisons to distinguish newly evaluated controls from actual configuration drift. Prioritize failed mandatory controls that are externally exploitable, weaken identity assurance, expose data or remove incident visibility. Route license-dependent findings to architecture and procurement owners as well as security.
Use staged change control for remediation. Conditional Access, PIM, external sharing, mail filtering and DLP can affect business workflows. The site’s Microsoft Entra PIM migration guide is a useful reminder that identity-control changes need API, automation and rollback validation.
Hands-on lab: precheck a legacy YAML file offline
This lab is intentionally local and read-only. It does not authenticate to Microsoft 365, install PowerShell modules or rewrite configuration. It identifies obvious legacy references that require review against CISA’s official migration mapping.
Prerequisites and isolated environment
- Python 3.9 or later on a non-production workstation.
- A new empty directory containing a copy of the YAML file. Remove tenant IDs, domains, user names and secret values first.
- The official CISA migration document open for manual review.
Create legacy-config.yaml:
ProductNames:
  - aad
  - defender
  - sharepoint
Defender:
  OmitPolicies:
    - MS.DEFENDER.2.1v1
Annotations:
  MS.EXO.16.1v1: "Approved exception pending review"
Save this as scubagear_v2_precheck.py:
#!/usr/bin/env python3
import re, sys
from pathlib import Path

patterns = [
    ("LEGACY_PRODUCT", re.compile(r"^s*-s*defenders*$", re.I)),
    ("LEGACY_SECTION", re.compile(r"^Defenders*:s*$", re.I)),
    ("LEGACY_POLICY", re.compile(r"bMS.(?:DEFENDER|EXO|TEAMS).[A-Z0-9.]+vd+b", re.I)),
]

text = Path(sys.argv[1]).read_text(encoding="utf-8").splitlines()
findings = []
for number, line in enumerate(text, 1):
    for kind, pattern in patterns:
        match = pattern.search(line)
        if match:
            findings.append((number, kind, match.group(0).strip()))

if not findings:
    print("PASS no obvious ScubaGear v1 Defender references found")
    print("NOTE validate the complete YAML with ScubaGear v2 before use")
    raise SystemExit(0)

print("REVIEW ScubaGear v2 migration items found")
for number, kind, value in findings:
    print(f"line={number} type={kind} value={value}")
print("ACTION use CISA's migration mapping; do not auto-rewrite policy IDs")
raise SystemExit(1)
Run the precheck:
python3 scubagear_v2_precheck.py legacy-config.yamlExpected output:
REVIEW ScubaGear v2 migration items found
line=3 type=LEGACY_PRODUCT value=- defender
line=5 type=LEGACY_SECTION value=Defender:
line=7 type=LEGACY_POLICY value=MS.DEFENDER.2.1v1
line=9 type=LEGACY_POLICY value=MS.EXO.16.1v1
ACTION use CISA's migration mapping; do not auto-rewrite policy IDs
An exit code of 1 means review is required. A pass only means the simple legacy patterns were not found; it does not prove that the YAML is valid or that every policy mapping is correct.
Troubleshooting and cleanup
- If the script reports a missing file, confirm the path and run it from the lab directory.
- If comments follow
defenderon the same line, use the downloadable version of the helper or remove the comment from the sanitized copy. - If the file uses anchors, templates or generated YAML, validate the rendered configuration with ScubaGear instead of relying on text matching.
- Never auto-rewrite legacy policy IDs without checking CISA’s mapping and the control’s changed meaning.
cd ..
rm -r scubagear-v2-precheck-lab
Check the current directory and folder name before cleanup. If the sanitized YAML still contains operational details, follow the organization’s retention and secure-deletion policy.
How to turn findings into durable evidence
- Keep raw outputs: preserve the original HTML, JSON and CSV before analysts annotate or transform them.
- Record applicability: note tenant type, licenses, product scope and controls that cannot apply.
- Separate failure from collection error: investigate API, permission and throttling errors before declaring a control failed or passed.
- Expire exceptions: every exclusion, omission or annotation should have an owner, approval, reason and review date.
- Compare over time: use consistent configuration and tool versions, then review diffs for drift and baseline changes.
- Validate remediation: rerun the affected product after change control and retain before-and-after evidence.
Common mistakes to avoid
- Treating a report as certification. ScubaGear compares observed settings with a baseline; it does not certify the organization or eliminate contextual risk analysis.
- Using v1 YAML unchanged. Version 2.0 rejects the Defender product and requires Security Suite migration.
- Marking license-dependent controls as passed. An unavailable feature is an architectural gap that needs a documented alternative or risk decision.
- Changing production from the report workstation. Keep assessment permissions and remediation privileges separated.
- Comparing totals without policy context. A different number of failures can reflect new or retired checks, not tenant drift.
Conclusion
ScubaGear 2.0 is most valuable when it becomes part of a repeatable Microsoft 365 assurance process rather than a one-time score. Preserve the old evidence, migrate Defender references carefully, confirm the tenant and permissions used, run the updated baseline, and route each finding to the service owner who can validate and remediate it.
The new Security Suite, risky-agent and SharePoint sharing checks make the release timely for both security teams and Microsoft 365 administrators. The durable outcome is not a perfect dashboard. It is traceable evidence that settings were assessed, exceptions were owned, changes were validated and drift will be found again.