CVE-2026-119756 is a newly published memory-corruption vulnerability in Tasmota Device Groups processing. An unauthenticated attacker who can reach the affected UDP service from the local network may be able to crash an ESP8266 or ESP32 device and potentially execute native code. The fix exists in the Tasmota source tree, but the project’s release page still lists version 16.0.0—the highest affected release—as current. Defenders should therefore inventory firmware provenance, restrict Device Groups traffic and verify that any replacement build actually contains the fixing commit.
Immediate priority: identify Tasmota devices running 16.0.0 or earlier, determine whether Device Groups are enabled, and block UDP 4447 from user, guest and untrusted IoT segments while a verified fixed build is prepared.
What the CVE record confirms
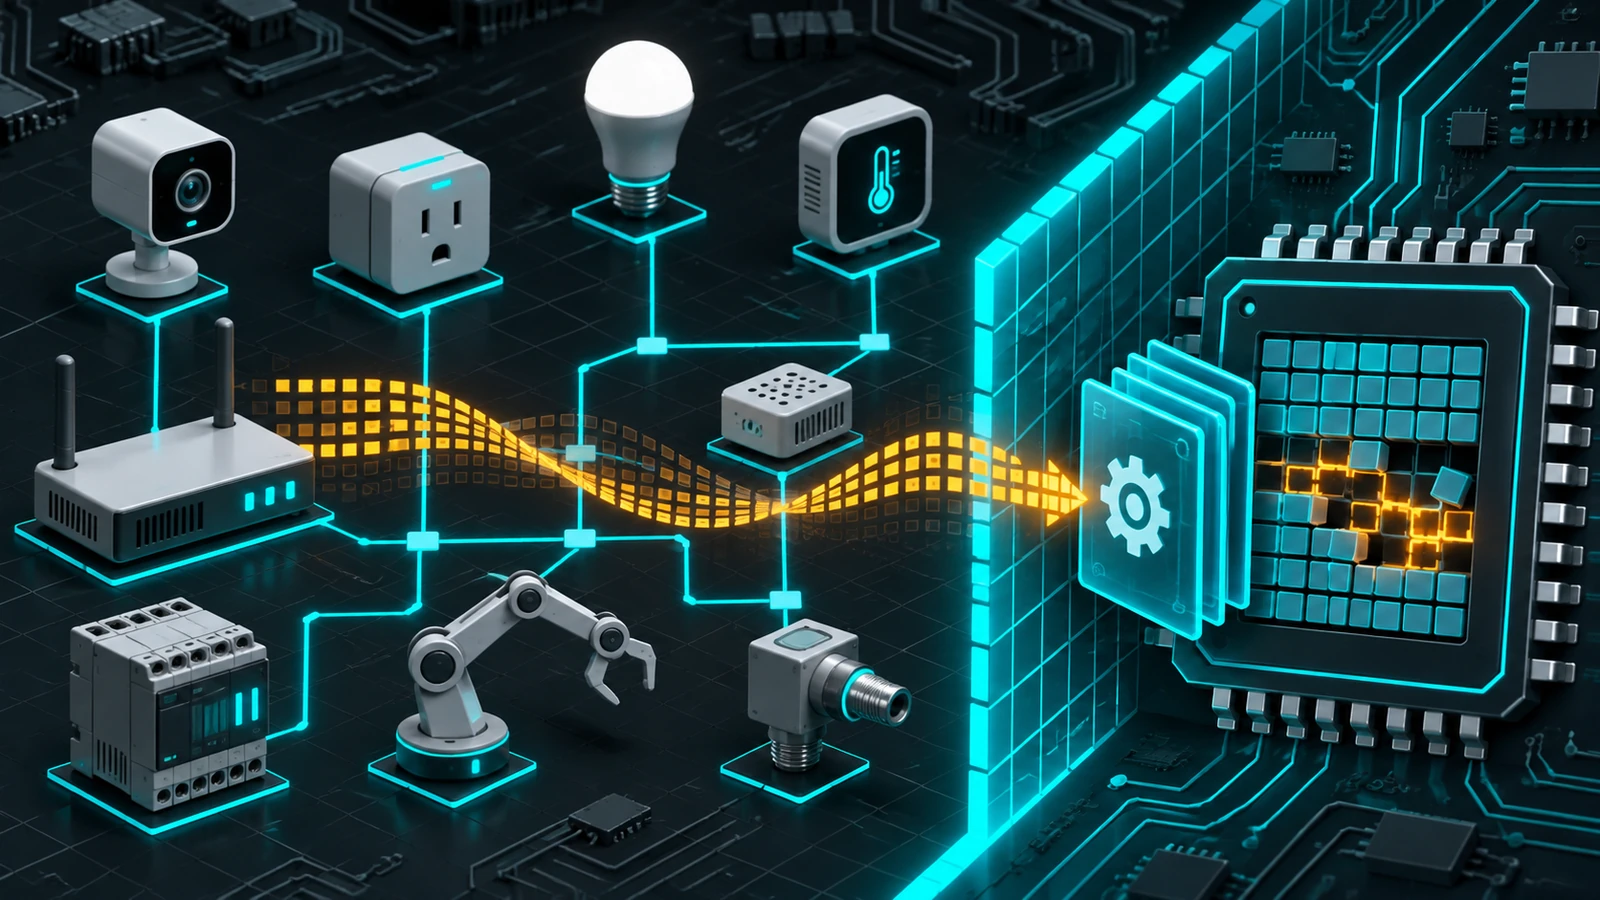
The CVE record was published on November 9, 2026 and covers Tasmota releases through 16.0.0. It identifies SendReceiveDeviceGroupMessage() as the affected routine and describes an out-of-bounds heap write caused by incorrect remaining-length handling while processing crafted Device Groups messages over UDP port 4447.
- Identifier: CVE-2026-119756
- Affected software: Tasmota through version 16.0.0
- Attack position: an unauthenticated system with network reachability to the affected local UDP service
- Potential impact: device crash and possible native code execution
- Fix reference: source commit
e97e1e4f7e319a55caa1613aef1f25fc81bdb554
The assigning CNA published CVSS 4.0 and CVSS 3.1 scores of 9.3 and 9.8 respectively. Those are vendor-record values, not scores calculated by this article. The reviewed primary and project sources do not confirm exploitation in the wild, and the vulnerability is not presented here as a CISA Known Exploited Vulnerability.
Why a local-network flaw can still be critical
“Local network” does not mean “trusted.” Enterprise IoT VLANs often contain devices from multiple vendors, unmanaged installer laptops, temporary gateways and long-lived Wi-Fi credentials. A compromised camera, building controller or guest-connected endpoint can become the foothold that reaches another device on the same broadcast domain.
Device Groups are designed to keep Tasmota devices synchronized without requiring every update to pass through an external application. That convenience creates an east-west communication path. If a malformed message reaches the vulnerable parser, the memory-safety boundary is crossed before administrator credentials or the web interface are relevant.
The risk is operational as well as technical. Smart plugs, lighting controllers, meters and relay modules may control physical processes. A crash can interrupt automation; code execution could also undermine device integrity or provide a durable position inside an IoT segment. Incident planning should therefore include safe power-state handling and an owner who understands what each device controls.
The release-status trap
The fixing commit changes one source file and replaces unbounded or incorrectly bounded logging operations with safer length handling. However, a source commit and a packaged release are not interchangeable. At the time of research on November 10, the official Tasmota documentation and GitHub release page both identify 16.0.0 as the current release, and 16.0.0 is inside the affected range.
Do not label a device “patched” only because it reports a version newer than 16.0.0. Confirm the firmware’s build provenance and verify that it contains commit e97e1e4 or an official release that explicitly incorporates that change. Custom builds deserve the same scrutiny: record the source revision, build configuration, binary hash and signer or trusted distribution path.
| Observed firmware | Interpretation | Action |
|---|---|---|
| 16.0.0 or earlier | Inside the published affected range | Segment now; prepare a verified fixed build |
| Build explicitly tied to e97e1e4 or later | Fix source is present | Validate build provenance and device behavior |
| Version number above 16.0.0 without provenance | Fix inclusion is unproven | Verify changelog, source revision and binary source |
| Unknown or vendor-rebadged firmware | Exposure cannot be determined | Escalate to owner or supplier; isolate meanwhile |
Defender response plan
1. Build a device-level inventory
- Record the hostname, IP address, MAC address, hardware model, ESP platform, firmware version and build identifier.
- Identify whether Device Groups are configured and which devices share a group.
- Map the VLAN, wireless SSID, firewall zone and every network that can send UDP traffic to the device.
- Assign a business owner and document the relay, lighting, metering or automation function that may be interrupted during maintenance.
- Export a supported configuration backup before changing firmware, as recommended by Tasmota’s upgrade guidance.
Use passive sources first: DHCP leases, wireless-controller inventories, switch MAC tables, DNS records, MQTT client identities and existing configuration management. Avoid aggressive scanning of constrained devices during production hours. The site’s broader enterprise IoT security guide explains why ownership and network boundaries are as important as firmware versions.
2. Reduce reachability immediately
- Block UDP 4447 from user, guest, server and unrelated IoT networks.
- Allow only the minimum same-group communication required for operations, ideally with source and destination restrictions.
- If Device Groups are not required, disable the feature through a supported maintenance procedure and verify that traffic has stopped.
- Prevent direct internet exposure of Tasmota management and local-control services.
- Keep recovery access available in case a firmware or configuration change causes a boot loop.
Segmentation is risk reduction, not a substitute for the fix. A compromised peer in the allowed group may still have the necessary reachability. Treat the temporary rules as containment controls and track them to removal or redesign after verified remediation.
3. Move to a verified fixed build
Prefer an official Tasmota release that explicitly states it includes the fixing commit. If operational urgency requires a source build, use a controlled and reviewed pipeline: pin the exact repository revision, preserve the build manifest, verify dependencies, sign or hash the artifact, test on representative spare hardware, and retain a recovery image. Do not download an arbitrary binary merely because its filename claims to be patched.
Follow the project’s documented migration path. Tasmota warns against upgrading from a minimal image directly to another minimal image and recommends backing up settings before an upgrade. Validate device templates, GPIO assignments, rules, timers, MQTT connectivity and safe relay state after flashing.
4. Hunt for signs of disruption or compromise
There is no authoritative public IOC list in the reviewed sources, so detection should be behavior-based. Examine firewall, switch, wireless, DNS, DHCP, MQTT and automation-platform telemetry around unexpected device failures.
- Unexpected UDP 4447 traffic from user, guest or newly connected IoT addresses
- Bursts of Device Groups traffic inconsistent with normal state changes
- Repeated reboots, watchdog resets, loss of MQTT connection or sudden DHCP renewals
- Configuration changes, new rules, altered MQTT brokers or unfamiliar firmware build identifiers
- New outbound connections from devices that normally communicate only with local automation services
A reboot is not proof of exploitation; power quality, Wi-Fi instability and ordinary firmware defects can produce similar symptoms. Correlate device behavior with network traffic and configuration changes. If compromise is plausible, isolate the device, preserve the running configuration and relevant network logs, then reflash from a trusted artifact and rotate credentials or broker tokens accessible to that device.
Hands-on lab: create a safe remediation queue
This offline lab classifies a sanitized CSV inventory. It does not scan devices, send UDP packets, generate exploit traffic or change firmware. Run it on a workstation with Python 3.9 or newer.
Create the isolated workspace
mkdir -p tasmota-triage-lab
cd tasmota-triage-lab
python3 --version
Create inventory.csv:
asset,firmware,device_groups,zone,udp_4447_from_user_lans,owner
lab-light-01,16.0.0,yes,iot-lab,yes,facilities
office-plug-07,15.6.0,yes,iot-prod,no,facilities
meter-02,16.0.0,no,iot-prod,no,energy
test-node,source-e97e1e4,no,isolated-lab,no,research
pilot-sensor,16.1.0,yes,iot-pilot,no,engineering
legacy-relay,unknown,unknown,legacy-iot,yes,unassigned
Create tasmota_inventory.py:
#!/usr/bin/env python3
import csv, sys

FIX_COMMIT = "e97e1e4"
AFFECTED_MAX = (16, 0, 0)

def version(value):
    parts = value.strip().lower().lstrip("v").split(".")
    if len(parts) < 2 or any(not item.isdigit() for item in parts):
        raise ValueError
    parsed = tuple(int(item) for item in parts[:3])
    return parsed + (0,) * (3 - len(parsed))

def enabled(value):
    return value.strip().lower() in {"yes", "true", "1", "enabled"}

def classify(row):
    firmware = row["firmware"].strip().lower()
    if FIX_COMMIT in firmware:
        return "FIX_PRESENT", "build identifies the fixing commit"
    try:
        current = version(firmware)
    except ValueError:
        return "REVIEW", "unknown firmware provenance"
    if current <= AFFECTED_MAX:
        if enabled(row["device_groups"]) and enabled(row["udp_4447_from_user_lans"]):
            return "ISOLATE_NOW", "affected, Device Groups enabled, UDP reachable"
        if enabled(row["device_groups"]):
            return "PATCH_AND_SEGMENT", "affected with Device Groups enabled"
        return "PATCH_AND_VERIFY", "affected; confirm Device Groups stay disabled"
    return "VERIFY_FIX", "newer version; verify inclusion of commit e97e1e4"

with open(sys.argv[1], newline="", encoding="utf-8") as handle:
    rows = csv.DictReader(handle)
    print("STATUStASSETtFIRMWAREtZONEtOWNERtREASON")
    for row in rows:
        status, reason = classify(row)
        print(f"{status}t{row['asset']}t{row['firmware']}t"
              f"{row['zone']}t{row['owner']}t{reason}")
Run and interpret the classifier
python3 tasmota_inventory.py inventory.csvExpected classifications:
ISOLATE_NOW      lab-light-01
PATCH_AND_SEGMENT office-plug-07
PATCH_AND_VERIFY meter-02
FIX_PRESENT      test-node
VERIFY_FIX       pilot-sensor
REVIEW           legacy-relay
FIX_PRESENT means only that the inventory identifies the fix commit; validate the artifact and device after deployment. VERIFY_FIX intentionally prevents a future-looking version string from being treated as proof. Replace the sample rows only with authorized inventory data and send unresolved assets to a named owner.
Troubleshooting and cleanup
IndexErrorusually means the script was run without the CSV filename.KeyErrormeans a required CSV header was changed or omitted.- If a firmware value is vendor-rebadged or abbreviated, leave it for human review rather than guessing.
cd ..
rm -rf tasmota-triage-lab
Post-remediation verification
- Confirm the installed artifact maps to the fixing commit or a release that includes it.
- Verify the device boots reliably and reports the expected firmware build.
- Test GPIO mappings, relay safety, rules, timers, MQTT and automation integrations.
- Confirm Device Groups behavior only where required and recheck UDP reachability from untrusted zones.
- Retain network restrictions that enforce the intended IoT trust boundary.
For a procurement and lifecycle view, use the site’s NIST IoT product security audit guide to record update mechanisms, support commitments, configuration recovery and evidence requirements for every device family.
Conclusion
CVE-2026-119756 turns a local Device Groups message into a memory-safety problem on constrained hardware. The fix is available in source, but defenders should not confuse a commit with a released and verified firmware artifact. Inventory the fleet, segment UDP 4447, disable unnecessary group communication, prepare a trusted build or official fixed release, and validate both device safety and network behavior after remediation.