Suricata 8.0.7 Security Upgrade: Validate Rules and EVE Telemetry
A practical SOC guide to upgrading Suricata 8.0.7, validating rules and parsers, checking EVE JSON telemetry, and testing an offline event stream.
A practical SOC guide to upgrading Suricata 8.0.7, validating rules and parsers, checking EVE JSON telemetry, and testing an offline event stream.
A defender-focused analysis of CISA AA26-281A, with detection priorities, response actions and a safe synthetic log-triage lab.
A practical control map for Microsoft’s five AI agent risk classes, with implementation guidance and a safe offline policy-audit lab.
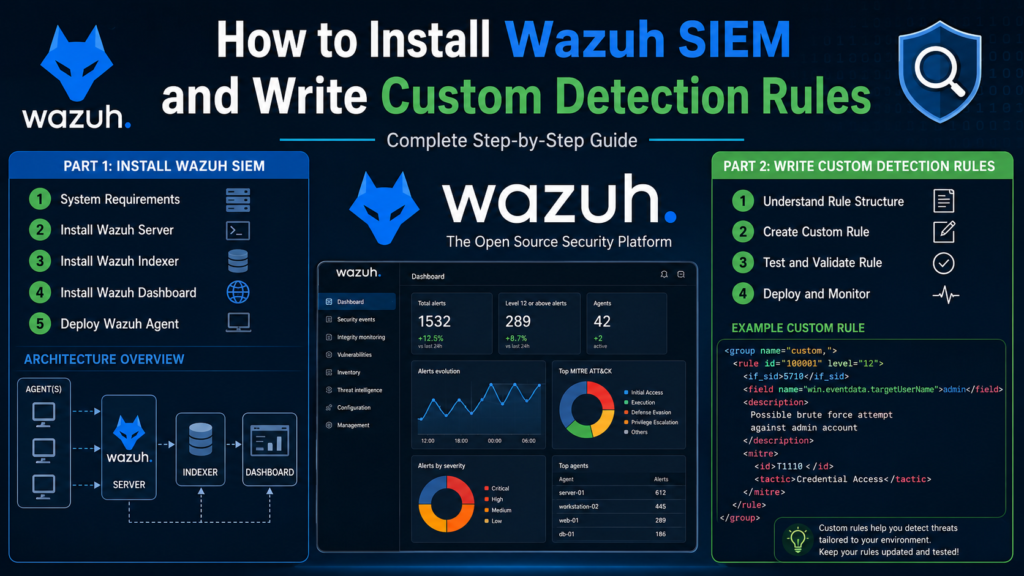
Install Wazuh SIEM on one host, enroll agents, and write custom detection rules that survive upgrades. Step-by-step 2026 tutorial with tested commands.
Advanced SOC operations 2026: proactive threat hunting methodologies, SOAR automation playbooks, Detection-as-Code with Sigma, purple team exercises, and analyst KPI metrics.