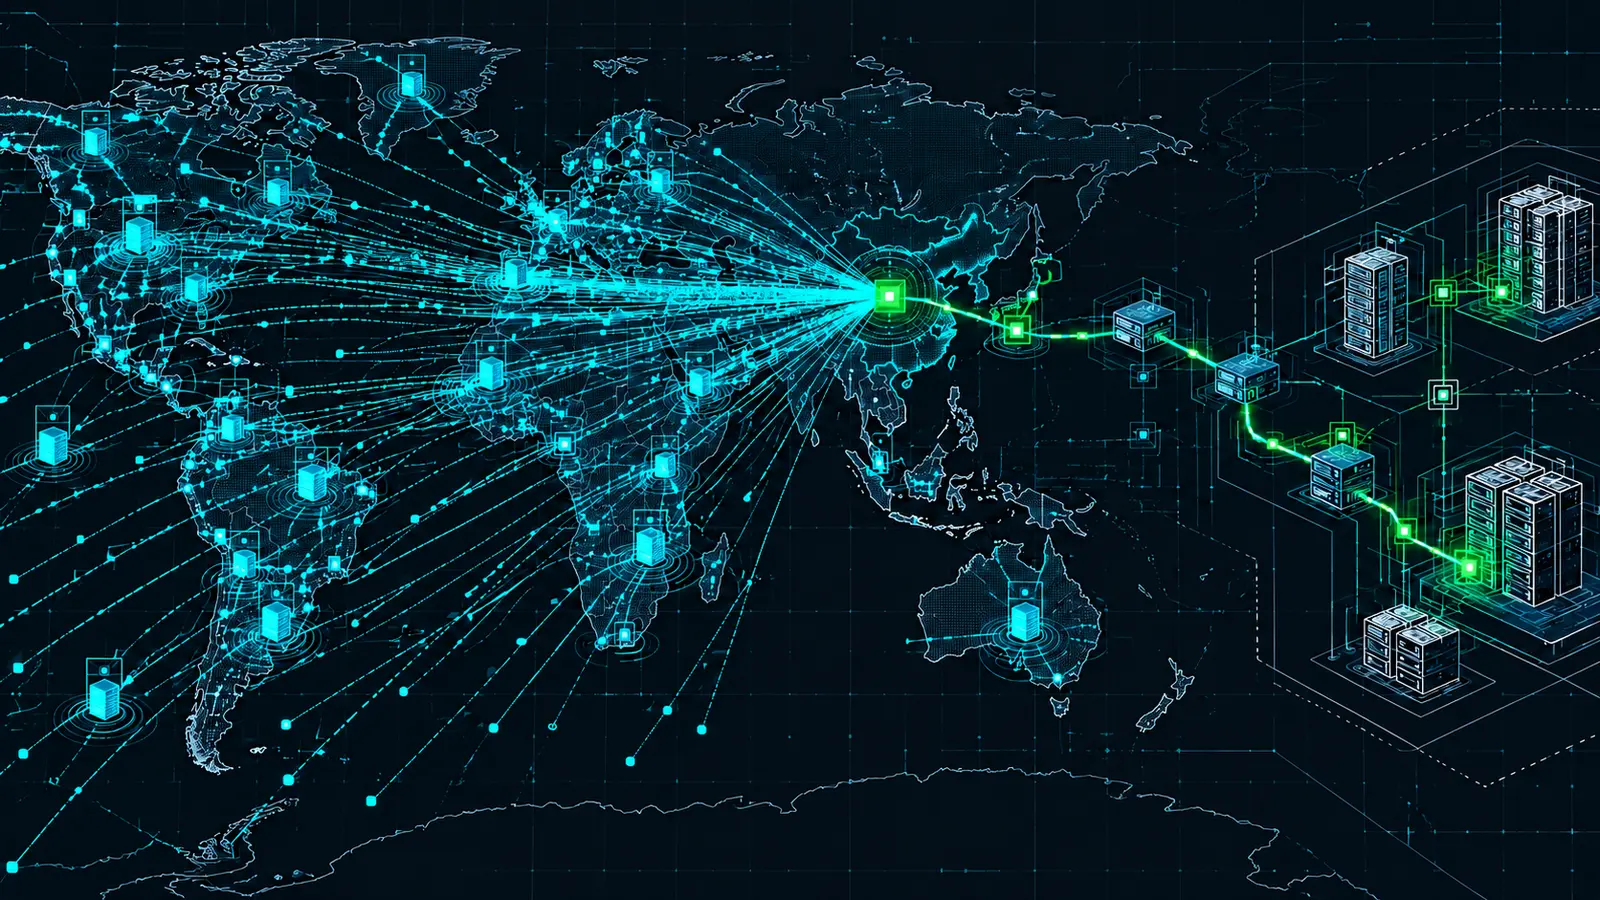
On October 8, 2026, CISA, the FBI, NSA and international partners published AA26-281A, a joint advisory describing how Chinese government-linked actors enabled by Integrity Technology Group combine internet-scale automation with hands-on intrusion work. The important lesson for defenders is not one malware family or one IP address. It is the transition from broad scanning and password attacks to tailored persistence, credential theft and email collection inside selected environments.
The advisory draws on evidence recovered during multiple FBI investigations and covers activity against government, critical manufacturing, healthcare, information technology, law enforcement, education and religious organizations. It maps the activity to MITRE ATT&CK and publishes a large set of indicators, but defenders should treat those indicators as starting points. Much of the tradecraft relies on legitimate tools, cloud interfaces and common administration paths that can outlive any single domain or hash.
What AA26-281A adds to the threat picture
The authoring agencies attribute the enabling infrastructure and tooling to Integrity Technology Group, a China-based company described as having links to the Chinese government. They note overlap with activity tracked publicly as Flax Typhoon, Ethereal Panda and Red Juliett, while warning that commercial and government naming systems are not exact one-to-one matches.
The operation begins with breadth. Actors use tools such as masscan, Nmap, WPScan, dirsearch and a Python web application called MicroScan. According to the advisory, MicroScan contains more than 1,300 penetration-testing scripts and has been used to look for weaknesses in products including WordPress, Jenkins, Apache Struts, Oracle WebLogic, OpenSSL and Juniper ScreenOS. The scanning focus includes ports 21, 22, 53, 80, 443 and 1080, plus PHP and ASP.NET page enumeration.
Once a promising target appears, the workflow becomes more selective. The documented activity includes exploit utilities written in Python and Go, cross-site scripting used for credential harvesting, password guessing and spraying against Microsoft Exchange, DCSync-style Active Directory replication, VPN-based persistence and automated email collection. This is why simply blocking a known scanner address is insufficient: the initial probe is only the first stage of a longer operator-driven chain.
The attack chain defenders should model
1. Reconnaissance at machine speed
Open-source scanners and large botnets let an operator test many organizations quickly. The tools themselves are dual-use, so a single Nmap-like pattern is weak evidence. The useful signal comes from context: repeated discovery across several services, enumeration of technology-specific paths, authentication attempts that follow scanning, or the same source infrastructure touching unrelated internet-facing applications.
2. Access through exposed services and identities
The advisory lists exploitation of older vulnerabilities, XSS-based credential harvesting and Exchange password attacks. The affected-product list includes CVE-2014-6278, CVE-2015-3306, CVE-2015-5477, CVE-2016-3081, CVE-2019-11510, CVE-2021-22205, CVE-2021-3199 and CVE-2023-22894. That range matters: exposure management has to include forgotten appliances, legacy services and applications that sit outside the normal server patch cycle.
3. Persistence hidden inside legitimate VPN software
Investigators observed SoftEther VPN clients downloaded with PowerShell on Windows or curl and wget on Linux. The clients were configured to reconnect at startup and were sometimes renamed conhost.exe or dllhost.exe. Those names normally belong to Windows components, so an alert based only on the filename can be misleading. Defenders should compare the file’s signer, original filename, hash, install path, service configuration and network destination.
4. Collection that resembles authorized access
The actors used a PHP script identified as Curlc4.txt to access Microsoft Exchange Web Services, compress email and upload it to remote infrastructure. The advisory also describes office-cli, a Linux command-line utility that uses configuration values such as client ID, tenant ID and secret to access Microsoft 365 mailboxes. Because those flows can use legitimate protocols and application credentials, mailbox auditing and cloud application governance are essential parts of endpoint-focused detection.
Five detection priorities for SOC teams
- Correlate scanning with later identity activity. Build a short time-window correlation between multi-port or directory enumeration and authentication failures against VPN, webmail, SSH or administrative interfaces. Track distinct usernames per source, not just attempts per account.
- Hunt for renamed VPN clients. Search process and file telemetry for
conhost.exeordllhost.exeoutside expected Windows directories, mismatched original filenames, unexpected SoftEther strings, new autoruns or outbound sessions from servers that do not normally run VPN clients. - Baseline directory replication. Alert when non-domain-controller systems or unexpected accounts request directory replication. Review the source host, account privileges and surrounding credential-access events before containment.
- Audit connected cloud applications. Inventory service principals and OAuth applications with mailbox or file access. Investigate new credentials, unusual tenant or client identifiers, broad consent and sustained mailbox reads from unfamiliar infrastructure.
- Watch outbound volume and staging behavior. Flag unusual uploads from low-egress hosts, archive creation near web or mail data, suspicious files in writable web directories and processes that rename themselves or run from temporary paths.
Do not turn the full IOC appendix into a permanent blocklist without validation. The advisory includes historical infrastructure and compromised systems with first-seen and last-seen dates. Age, ownership and local context matter. A better workflow is to tag matches as enrichment, then raise confidence when an indicator is paired with a relevant behavior such as VPN persistence, password spraying or email collection.
Response and hardening checklist
- Inventory internet-facing services and close unused ports, remote administration paths and file-sharing protocols.
- Patch supported software and firmware, and replace end-of-life products that cannot receive security updates.
- Require phishing-resistant MFA where available, especially for webmail, VPN and privileged access.
- Review administrative accounts and service credentials for least privilege; rotate exposed keys and secrets.
- Inspect web access logs for traversal, injection and enumeration patterns, not only successful HTTP responses.
- Monitor cloud accounts for newly connected applications with access to mailboxes or sensitive file stores.
- Segment edge systems from identity infrastructure and sensitive data so a compromised service cannot move freely.
- If compromise is suspected, preserve evidence, isolate affected hosts, scope identities and connected applications, and plan eviction before removing individual artifacts.
The agencies specifically recommend collecting enough threat-hunting evidence to choose effective countermeasures before completing eviction. That sequencing matters. Deleting one binary while the operator still holds an application secret, mailbox token or alternate VPN path can produce a false sense of containment.
Hands-on lab: triage three behaviors with synthetic logs
This lab is safe to run on an isolated workstation because it uses only synthetic JSON events. It does not scan networks, contact external infrastructure or reproduce an exploit. You need Python 3 and a new empty directory.
Create the sample telemetry
mkdir -p aa26-281a-lab && cd aa26-281a-lab
cat > lab_events.jsonl <<'EOF'
{"ts":"2026-10-09T07:40:00Z","type":"auth","source_ip":"198.51.100.24","user":"[email protected]","result":"failure"}
{"ts":"2026-10-09T07:40:08Z","type":"auth","source_ip":"198.51.100.24","user":"[email protected]","result":"failure"}
{"ts":"2026-10-09T07:40:15Z","type":"auth","source_ip":"198.51.100.24","user":"[email protected]","result":"failure"}
{"ts":"2026-10-09T07:41:02Z","type":"process","host":"ws-17","name":"conhost.exe","original_file_name":"vpnclient.exe","command_line":"C:\ProgramData\vpn\conhost.exe /connect demo"}
{"ts":"2026-10-09T07:42:10Z","type":"directory","host":"app-02","action":"directory-service-replication","source_user":"svc-backup"}
{"ts":"2026-10-09T07:45:00Z","type":"process","host":"ws-03","name":"notepad.exe","original_file_name":"notepad.exe","command_line":"notepad.exe notes.txt"}
EOF
Create the detector
#!/usr/bin/env python3
import json
import sys
from collections import defaultdict

path = sys.argv[1] if len(sys.argv) > 1 else "lab_events.jsonl"
events = []
with open(path, encoding="utf-8") as handle:
    for number, line in enumerate(handle, 1):
        try:
            events.append(json.loads(line))
        except json.JSONDecodeError as exc:
            print(f"WARN line={number} invalid_json={exc}", file=sys.stderr)

failures = defaultdict(set)
for event in events:
    if event.get("type") == "auth" and event.get("result") == "failure":
        failures[event.get("source_ip", "unknown")].add(event.get("user", "unknown"))

for source_ip, users in failures.items():
    if len(users) >= 3:
        print(f"ALERT password_spray source_ip={source_ip} distinct_users={len(users)}")

for event in events:
    if event.get("type") == "process":
        name = event.get("name", "").lower()
        original = event.get("original_file_name", "").lower()
        command = event.get("command_line", "").lower()
        renamed = name in {"conhost.exe", "dllhost.exe"} and original not in {name, ""}
        vpn_artifact = any(token in original + " " + command for token in ("vpnclient", "softether", "vpncmd"))
        if renamed and vpn_artifact:
            print(f"ALERT renamed_vpn_client host={event.get('host')} image={name} original={original}")
    if event.get("type") == "directory":
        if event.get("action") == "directory-service-replication" and event.get("source_user") not in {"dc01$", "dc02$"}:
            print(f"ALERT unexpected_directory_replication host={event.get('host')} user={event.get('source_user')}")
Save that code as detect_integrity_tech_patterns.py, then run it:
python3 detect_integrity_tech_patterns.py lab_events.jsonlExpected output:
ALERT password_spray source_ip=198.51.100.24 distinct_users=3
ALERT renamed_vpn_client host=ws-17 image=conhost.exe original=vpnclient.exe
ALERT unexpected_directory_replication host=app-02 user=svc-backup
The sample address belongs to the documentation-only TEST-NET-2 range. In production, replace the field names and thresholds with those from your identity provider, endpoint platform and directory audit source. A three-user threshold is intentionally low for the lab; tune it against normal help-desk activity, shared proxies and approved vulnerability scanners.
Troubleshooting and cleanup
- If Python reports invalid JSON, confirm each event occupies one line and that Windows backslashes remain doubled.
- If the VPN alert does not fire, verify both the displayed filename and the original filename fields are present.
- If your directory platform uses different event names, map its replication event to the lab’s
directory-service-replicationvalue.
cd ..
rm -r aa26-281a-lab
How to operationalize the advisory
Start with a behavior-to-data-source table rather than copying hundreds of indicators into a SIEM. For each behavior, name the log source, retention period, owner and a test case. Then validate whether controls can see active scanning, multi-account authentication failures, suspicious VPN persistence, unexpected directory replication and high-volume mailbox access. This follows the agencies’ recommendation to select an ATT&CK technique, align security technology, test it, analyze performance and tune the program.
For related workflows, see VigilSecureInfo’s CISA KEV prioritization pipeline, detection lessons from two SOC assessments and SOC threat-hunting and SOAR guide.
Conclusion
AA26-281A is valuable because it connects commodity-scale discovery to deliberate post-compromise operations. The most durable defense is therefore layered: shrink the public attack surface, strengthen identity controls, detect unexpected administrative behavior, govern cloud applications and test whether response teams can follow an intrusion across network, endpoint, directory and email telemetry. Use the published IOCs to enrich that work, not to replace it.
Primary sources
- CISA, AA26-281A, published October 8, 2026.
- FBI IC3, downloadable joint advisory PDF, published October 8, 2026.
- NSA press release and advisory link, published October 8, 2026.
- Australian Signals Directorate’s ACSC advisory mirror, published October 9, 2026.